Ugh Auth
An access-control layer for self-hosted applications, including HTTP and WebSocket traffic.
AI-generated concept illustration
Problem & context
Self-hosted applications need a clear authentication boundary without coupling every application to the same internal implementation.
My contribution
Built site-scoped sessions, forward authentication and HTTP/WebSocket proxying for applications that need an access-control layer.
Decisions & tradeoffs
Make invalid authentication and unsafe local configuration block access.
Handle configuration and proxy boundaries explicitly, with regression checks for important failure paths.
Keep the gateway small enough to run as one local process.
Use file configuration and site-bound sessions, without adding a hosted account service or database. Keep the frameworkless landing page separate from the authentication runtime.
Outcome
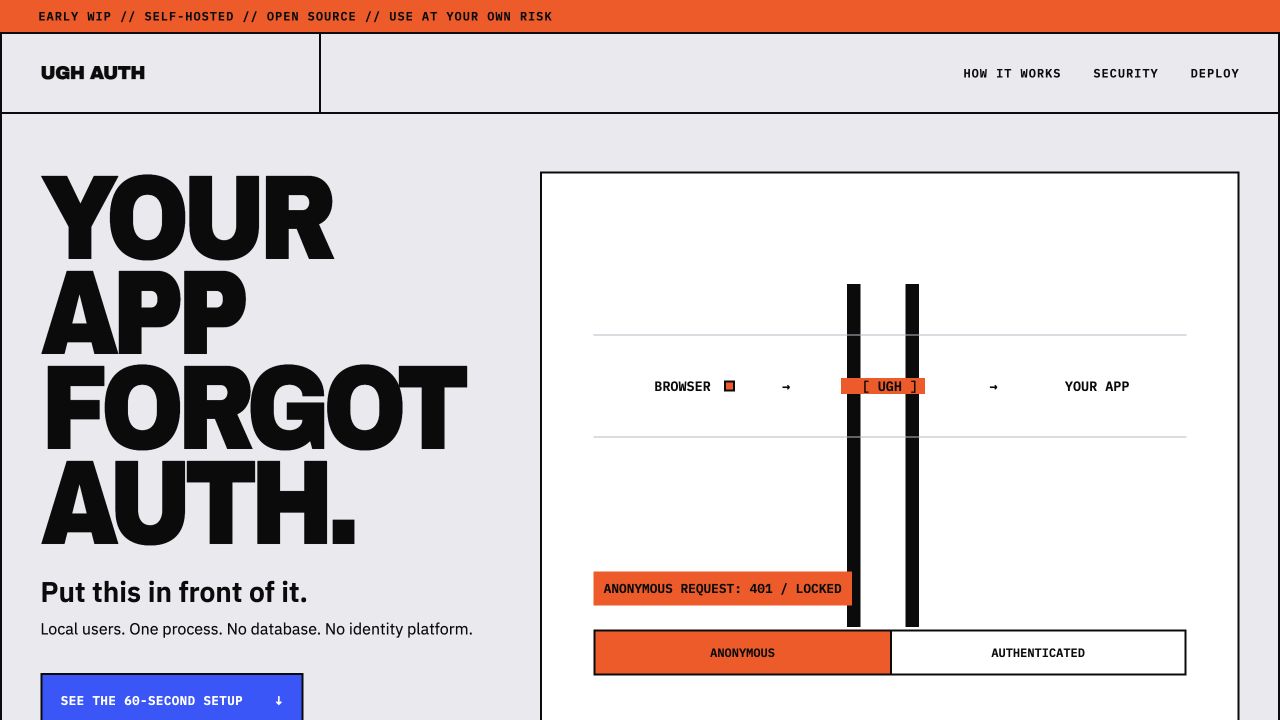
A small authentication gateway with site-scoped sessions and HTTP/WebSocket proxying, accompanied by an interactive landing page that explains the request flow.
Additional images